

October 2026
Cross App Access: Apps Linked at SSO Sign-In
Cross App Access creates a linked account for each person on each app you allow in your identity provider, when they sign in to StackOne through your SSO connection. It works with Okta and other identity providers that support Cross App Access. StackOne asks the identity provider for each person’s access to each app, so its policy decides who gets an app and who keeps it. When that person connects an AI platform, StackOne’s consent screen lists their linked accounts and no app asks for its own sign-in.
What’s new
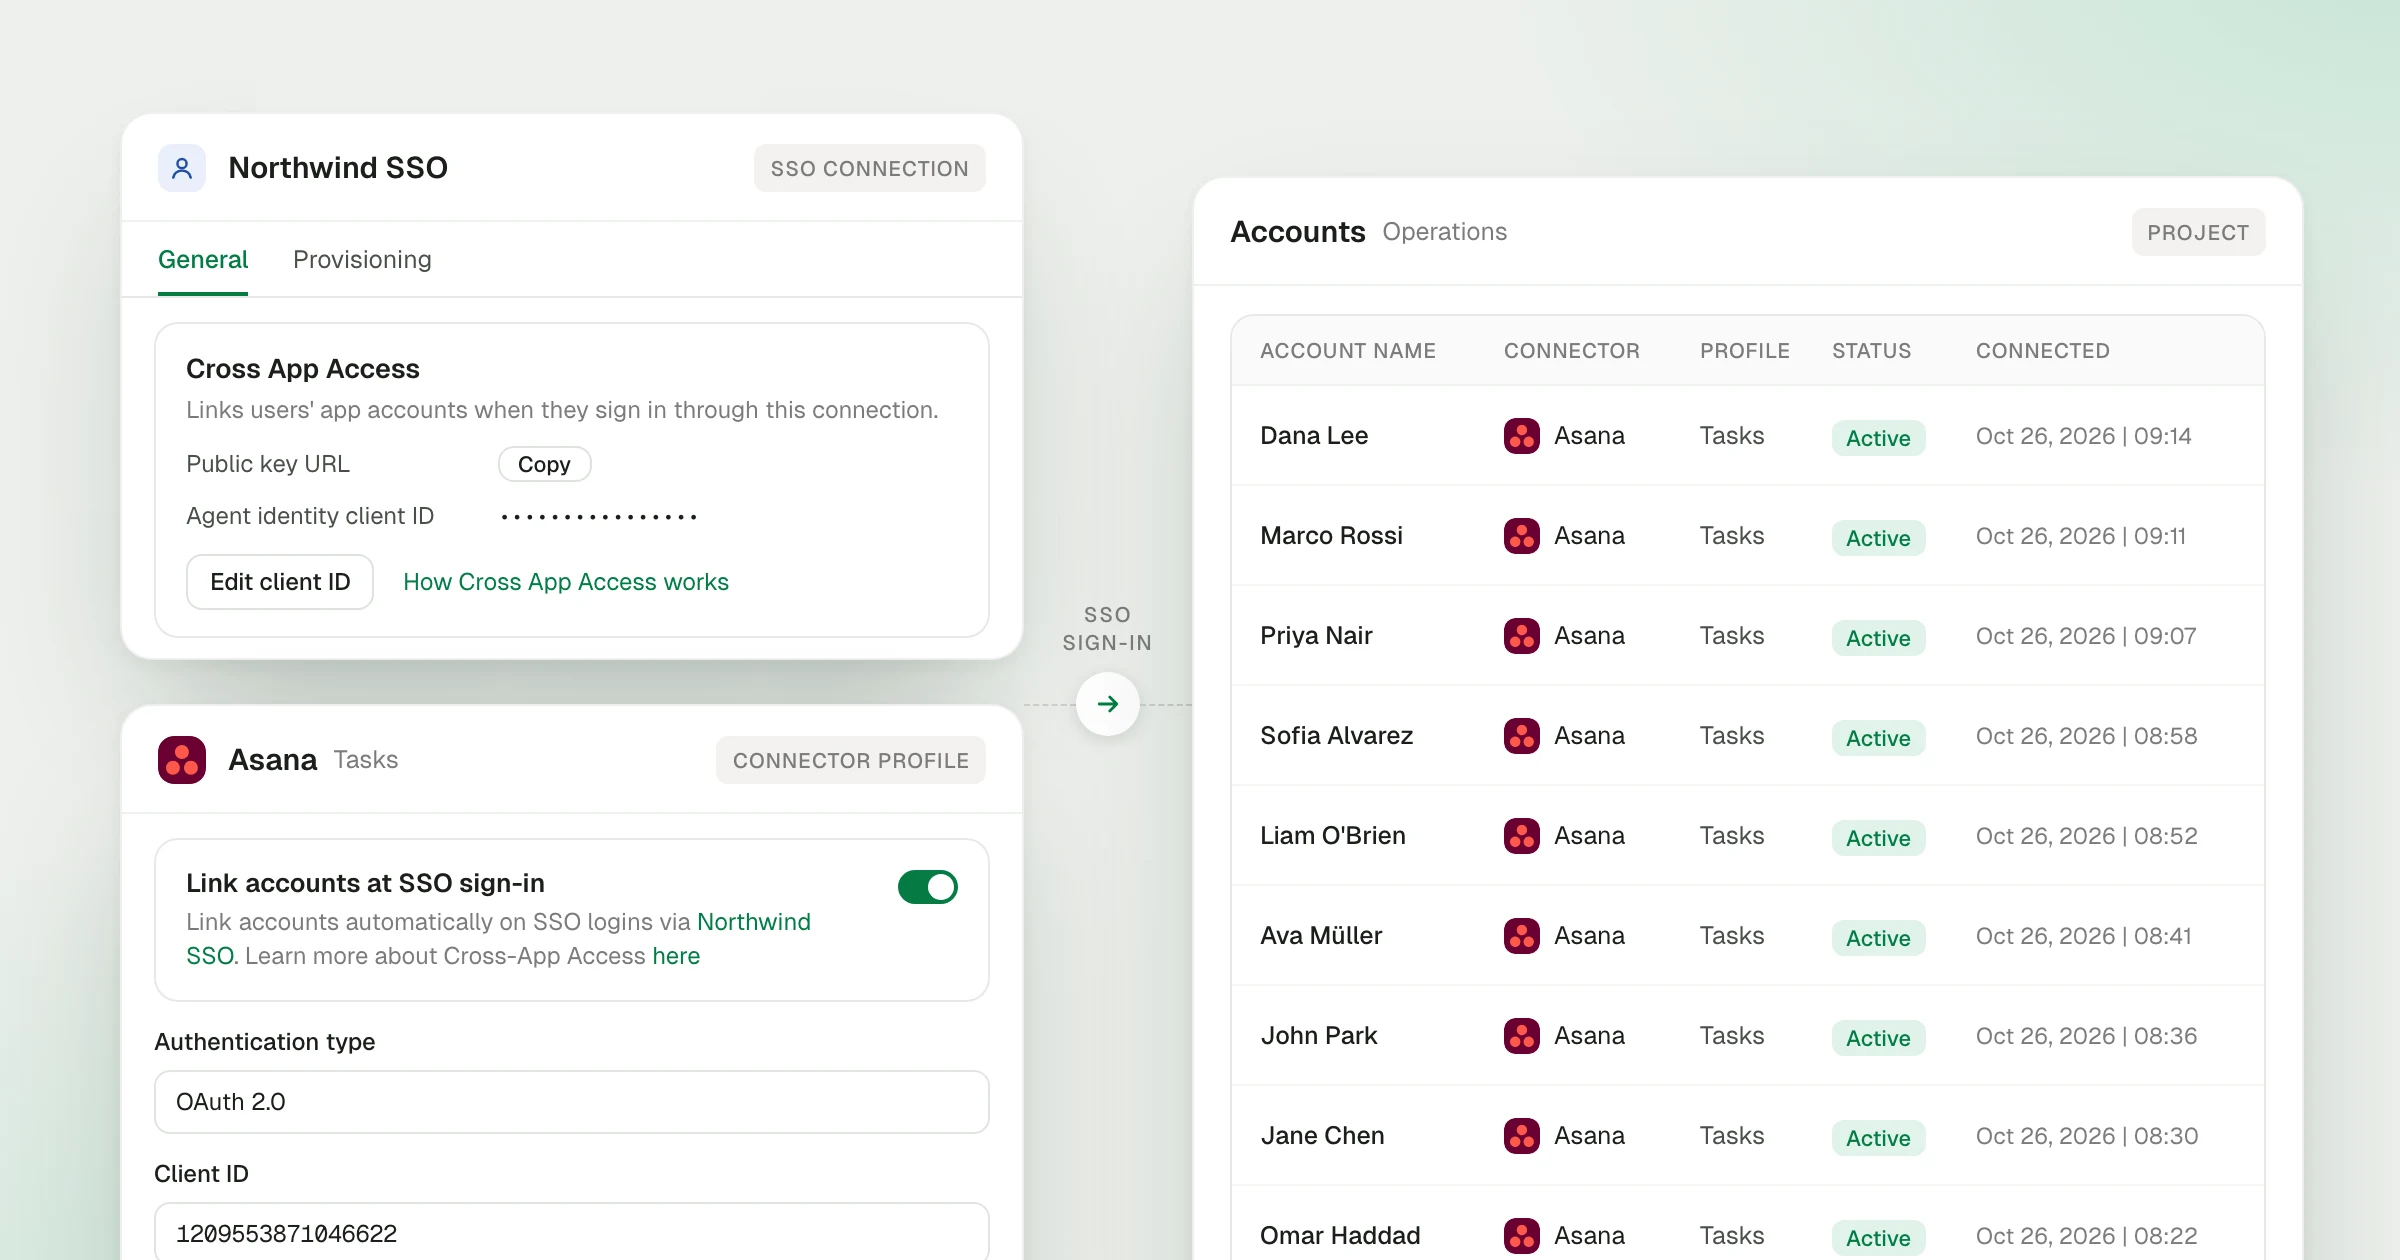
- Accounts linked at sign-in - At SSO sign-in, StackOne uses the signed SAML assertion to request the identity provider’s grant for each app, then links an account on every connector profile with Link accounts at SSO sign-in turned on. A new person’s first sign-in finishes with their apps already linked.
- Your identity provider grants the scopes - StackOne requests the scopes the connector profile requests, and the identity provider grants only what its policy allows for that person and app.
- Cross App Access card - The SSO connection’s General tab shows the Public key URL that your identity provider reads StackOne’s key from, and holds the Agent identity client ID you paste back from it.
- A switch on each connector profile - Link accounts at SSO sign-in is on by default for a new profile that uses an app’s OAuth or MCP option with your own client ID and secret. Turn it off to keep that app out of linking.
- Follows project roles and profile access - Project Admins and Project Members get linked accounts in their projects, and a Restricted profile links only for the users and groups it grants. People added by Just-in-Time provisioning or Directory Sync get the role set under Provisioned access.
- Access ends in your identity provider - Unassign a person in your identity provider, or remove StackOne’s access to an app there, and their access ends when the app’s current token expires. StackOne renews expired tokens through the identity provider, so its current policy applies.
Cross App Access runs on a SAML SSO connection, described in the Single Sign-On guide. The Cross App Access guide walks through both sides of the setup, in StackOne and in your identity provider.